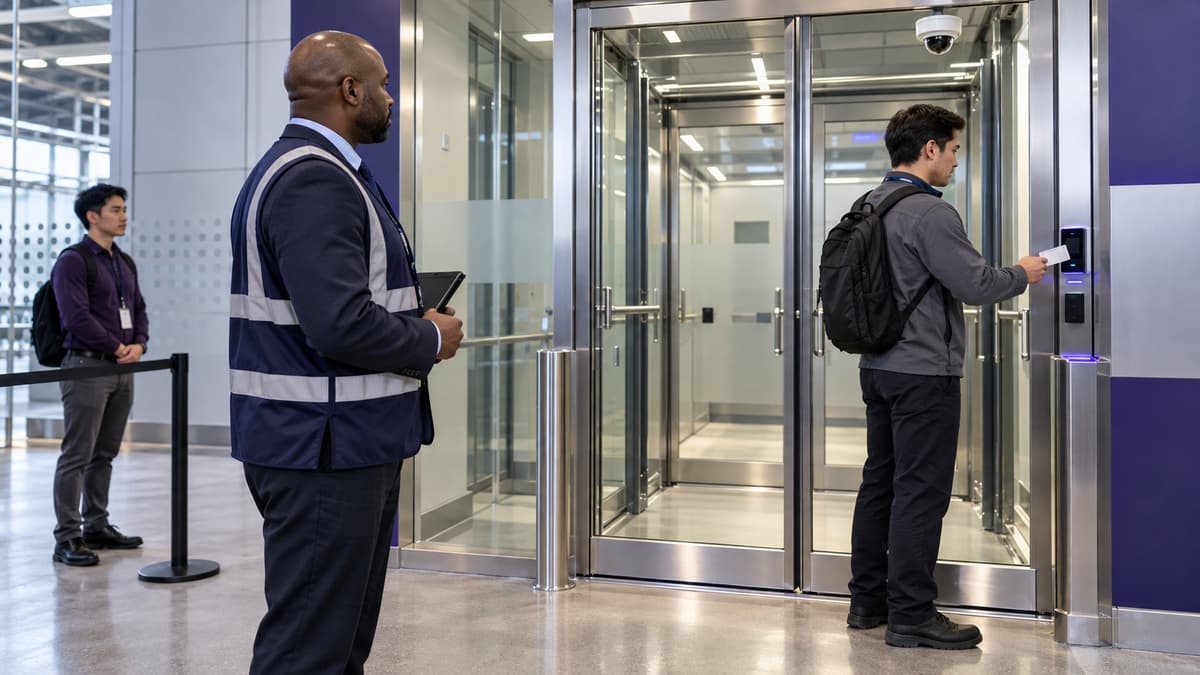
The Operational Question
Can a person enter a restricted data center zone without presenting the right credential, being challenged, or leaving a reviewable record? Security teams often know the answer in theory, but a policy review does not show whether a busy shift change, an open door, a delivery, or a helpful employee creates an unintended path into a white space, electrical room, network room, or control center. An anti-tailgating drill gives facility and security leaders a controlled way to test the complete chain: badge presentation, door hardware, mantrap behavior, guard response, camera coverage, alarm routing, and incident documentation.
This is a physical-facilities exercise, not a trap for employees. The objective is to find weaknesses before an unauthorized person uses them, while protecting life safety and keeping customers, contractors, and operations staff informed enough to avoid confusion. This guide explains how to define the test, coordinate it with operations, observe the result, and turn the findings into practical training and corrective work. It also shows how physical-security training can fit alongside a site’s operating procedures and audit program.
Who This Affects
The exercise matters anywhere a badge-controlled boundary protects critical equipment, customer areas, or sensitive records. The setting may be an enterprise data center, a multi-tenant colocation facility, a hyperscale campus, or an edge site with only a few people on shift. Each environment has a different traffic pattern, but the exposure is similar when people assume that a familiar face, a uniform, or a full cart is evidence of authorization.
The people who should help plan or review the drill include:
- Security leads who own access policy, guard instructions, visitor processing, camera review, and incident escalation.
- Facility managers who understand doors, locks, mantraps, loading areas, fire egress, and the effect of a test on building operations.
- Operations managers and NOC staff who may receive alarms or be asked to validate whether a restricted room is occupied.
- EHS and emergency-response leaders who need the exercise to respect evacuation routes, emergency exits, accessibility, and stop-work authority.
- Colocation customer representatives who can explain tenant escort rules without exposing customer-specific details.
- Contract security officers, maintenance technicians, electricians, cleaners, and delivery staff who encounter the actual workflow during a normal week.
The drill is especially useful during a new guard-contractor transition, after a badge-system change, when a new hall opens, after a door or camera modification, or when a site has experienced repeated propping, shared credentials, or unexplained access events. A site with no mantrap can still test the same principles at a vestibule, cage entrance, loading-door boundary, or two-door administrative checkpoint.
What Can Go Wrong
Tailgating is not limited to one person walking closely behind another. A person may enter when a badge holder holds a door for a cart, when a door fails to latch, when a visitor follows a contractor through a turnstile, or when a guard waves through someone whose credential was never checked. Piggybacking can also happen when two people present themselves as one approved group even though only one identity was verified.
The physical consequences can be serious. An unauthorized person may reach energized switchgear, UPS equipment, battery strings, generators, fire-protection controls, or cooling plant areas. They may be exposed to arc-flash, electrical, mechanical, refrigerant, or confined-space hazards. Even when no injury occurs, an unescorted person can interrupt maintenance, touch a control, remove a part, photograph a customer cage, or create uncertainty about whether the room is secure.
The operational and compliance consequences are broader than a single door event:
- An alarm that reaches a guard but not the responsible operations desk can remain unresolved during a busy shift.
- A camera may show entry but not capture the face, badge presentation, direction of travel, or person who opened the door.
- A shared badge or stale contractor credential can make the access log look legitimate while hiding the actual identity.
- A mantrap may allow both doors to open, or its interlock may be bypassed by a release button that staff use as a convenience.
- A report that says “security issue” without time, location, people involved, and evidence cannot support a useful corrective action.
- A poorly coordinated drill can startle employees, disrupt a customer, block egress, or make guards reluctant to report future weaknesses.
Standards and frameworks generally emphasize controlled access, least privilege, monitoring, and documented response. They do not replace the site’s own hazard assessment or operating procedures. A facility should map its chosen control objectives to the actual door hardware, staffing model, emergency release design, and customer commitments rather than claiming that one drill proves compliance with a framework.
What Managers Should Check
Treat the exercise as a small commissioning and incident-response test. Before anyone approaches a door, define what is being tested and how the team will stop the test if a real emergency occurs.
- Define the boundary and the expected behavior.
Choose one route, such as the employee entrance to a secure operations corridor, the visitor vestibule to a data hall, or the loading-area door to a mechanical room. Write down what should happen at each step: whose badge is required, whether a second person must present a credential, when a guard should challenge, what camera should record, and who receives an alarm. Do not leave the success condition as “the door stays secure.”
- Obtain the right approvals and exclusions.
Notify the site leader, security supervisor, facilities contact, and emergency coordinator. Exclude active emergency response, live electrical switching, customer-sensitive spaces, and any area where a test person could be mistaken for an intruder. Set a stop phrase or radio call that ends the exercise immediately. Do not disable a life-safety system to create a more dramatic scenario.
- Select a safe scenario.
Use a controlled role player and a credentialed participant who knows the drill. Examples include:
- A person follows a badge holder toward a mantrap without presenting a badge.
- A contractor arrives at a controlled entrance with a valid work order but an expired site badge.
- A cart or tool case causes the badge holder to hold the door open longer than normal.
- A door is found ajar during a patrol, and the guard must determine whether it is a fault, an approved hold-open, or an access event.
Avoid disguises, physical contact, threats, running, or attempts to defeat a lock. The point is to test recognition and response, not to simulate violence.
- Verify the technical path before the live attempt.
Confirm that the door closes and latches, the reader identifies the credential, and the access-control system records the event with a usable timestamp. Check that door-held-open and forced-door alarms are mapped to the correct location. Confirm that camera views include the face, badge reader, approach path, and the direction of travel. If the site uses a mantrap, verify that the interlock behavior and emergency-release function match the approved design.
- Test the human response.
Observe whether the guard or employee challenges the person in a professional, consistent way. The expected response may be a request to present a badge, a direction to the visitor desk, a call to the escort, or a pause while the credential is verified. It should not rely on recognizing a person from memory. Record how long it takes for the right person to notice, who owns the next action, and whether the response changes during a shift change or delivery rush.
- Check escalation and evidence.
After the attempt, compare the observer’s timeline with the access log, alarm history, radio traffic, guard notes, and camera footage. Look for clock drift, missing video, unclear naming, or an alarm that was acknowledged without a documented disposition. A good record should identify the location, date, scenario, observed behavior, people in approved roles, control result, and corrective owner without publishing sensitive badge numbers or customer information.
- Review the boundary around contractors and visitors.
Ask whether a visitor badge expires automatically, whether an escort is required for the entire route, and how temporary badges are recovered. Check that a work order, purchase order, or uniform is not treated as a substitute for identity and access authorization. For recurring vendors, compare the access list with current contracts, training status, and the work actually scheduled.
- Assign corrective actions with a retest date.
Separate hardware, configuration, procedure, and behavior findings. A door that does not latch needs a facilities or security-system repair. A camera pointed at the ceiling needs a technical correction. A guard who did not know the challenge procedure needs a briefing and practice. A policy that conflicts with the way carts move through the site needs an operational redesign. Give every action an owner, due date, risk priority, and verification method.
The manager’s final question should be simple: if the same condition appears tomorrow at 2:00 a.m., will the person on duty know what to do, have the tools to do it, and leave evidence that the response occurred?
Which Training Fits This Situation
The most direct course connection is Access Control & Physical Security. It fits security officers, facility staff, supervisors, and contractors who need a common understanding of credential handling, controlled entry, surveillance, and incident reporting. A role-based plan can use the same drill as the practical discussion point: security leads focus on challenge and escalation, facilities staff focus on doors and emergency release, and operations staff focus on alarm ownership and service continuity.
For a broader physical-security program, Security & Compliance for Data Centers helps managers connect access controls to audit readiness, facility procedures, and the evidence a site should organize. The live catalog also lists Data Center Physical Security and Access Control Training, which is a useful fit when the team needs focused coverage of facility entry, surveillance, and reporting workflows.
The Security & Compliance Bundle is appropriate when the site is building a fuller program rather than correcting one door. The bundle is described for security and compliance leads building an audit-ready physical security, fire safety, and environmental compliance program, and includes five online courses. It can provide a shared foundation for the people who design the drill, operate the checkpoint, review the evidence, and close corrective actions.
Training should support the site’s procedures, not replace a local access-control configuration review or an emergency plan. After learners finish, have them walk one representative route, identify the expected control at each boundary, and practice writing a concise incident record. That turns a course concept into a repeatable site habit.
Common Mistakes to Avoid
- Treating a successful badge read as proof that the second person was authorized.
- Testing during a real alarm, emergency response, critical switching task, or customer-sensitive activity.
- Asking a guard to improvise the challenge script instead of defining a respectful, safe response.
- Disabling interlocks, camera recording, or alarm routing without a documented technical review and restoration check.
- Using an employee’s real credentials as a surprise test without protecting privacy and explaining the record-retention plan.
- Measuring only whether the door opened. Include detection, challenge, escalation, evidence, and corrective action.
- Assuming a mantrap solves every problem while ignoring propped doors, emergency exits, loading docks, cages, and shared credentials.
- Writing a finding with no location, timestamp, owner, risk statement, or retest date.
- Promising that a course or drill grants a regulatory certification or proves compliance with an external standard. Courses provide knowledge and a certificate of completion; the facility remains responsible for its own program.
Key Takeaway
An anti-tailgating drill is valuable when it tests the whole control path: a person approaches, a credential is evaluated, a door or mantrap behaves correctly, someone notices an exception, the event reaches the right team, and the site can prove what happened afterward. The most useful result is not a perfect score. It is a specific finding that can be assigned, corrected, and tested again without putting people or uptime at risk.
This week, choose one badge-controlled boundary and schedule a fifteen-minute tabletop review with security, facilities, and operations. Walk through one approved tailgating scenario, compare the expected response with the actual system and procedure, and assign one owner to close the first gap.
Sources
- NIST, Security and Privacy Controls for Information Systems and Organizations, SP 800-53 Rev. 5
- NIST, Guide to Enterprise Telework, Remote Access, and Bring Your Own Device Security, SP 800-46 Rev. 2
- CISA, Physical Security Performance Goals
- NIST, Physical and Environmental Protection controls overview